Blog
That Big WordPress Security Scare: What It Means for Your Website (in Plain English)
Saw the scary PHP headlines and can't tell if your WordPress site is at risk? Here's what happened, how worried to be, and the one email to send your host today.
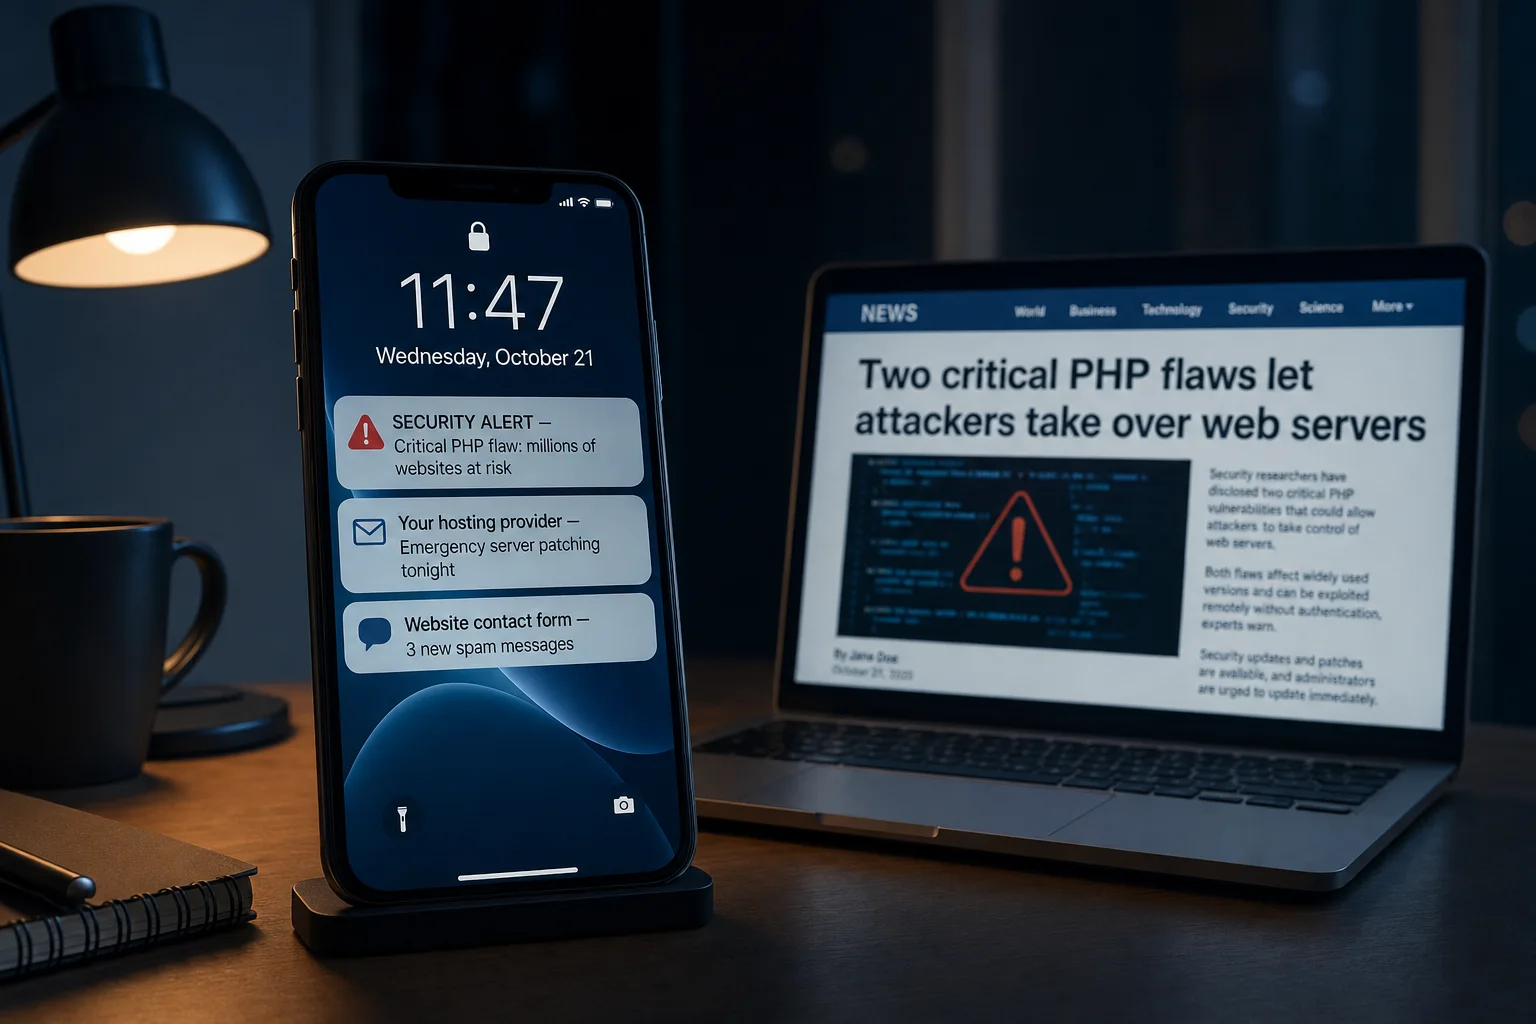
If you have a WordPress website, you've probably seen the headlines this week. "Critical." "Take over servers." "Patch now." They were full of version numbers and acronyms, and almost none of them said what a business owner is actually meant to do.
So here's what happened, how worried to be (a bit, not a lot), and one email to send today. Longer term, there are two ways out of alerts like this: keep WordPress and keep up with it, or move to a platform where there's nothing for you to patch, which is why we built Mondovo.
What happened?
Security researchers found two serious flaws in PHP. PHP is the behind-the-scenes software that WordPress runs on, along with millions of other websites. You've probably never had to think about it, and that's normal.
These flaws were rated about as serious as these things get. In the wrong hands, they could let someone take control of the computer your website runs on, without needing a password. Government security agencies in the US and Europe told organisations to fix it right away.
The people who look after PHP released a fix on 21 October 2026. That's the good news. The catch is that the fix doesn't install itself on every website. Somebody has to put it there.
Should I be worried?
A little, yes. Panic, no.
Whether your site is protected comes down to one thing: has someone actually installed the fix? For most small business owners, that someone is your hosting company or your web developer.
The sites most at risk are the ones nobody looks after:
- a site a freelancer built a few years ago and hasn't touched since;
- a cheap hosting plan that's still running old software; or
- a site where you aren't quite sure who's responsible for updates.
If one of those sounds like yours, set aside ten minutes this week.
What should I do today?
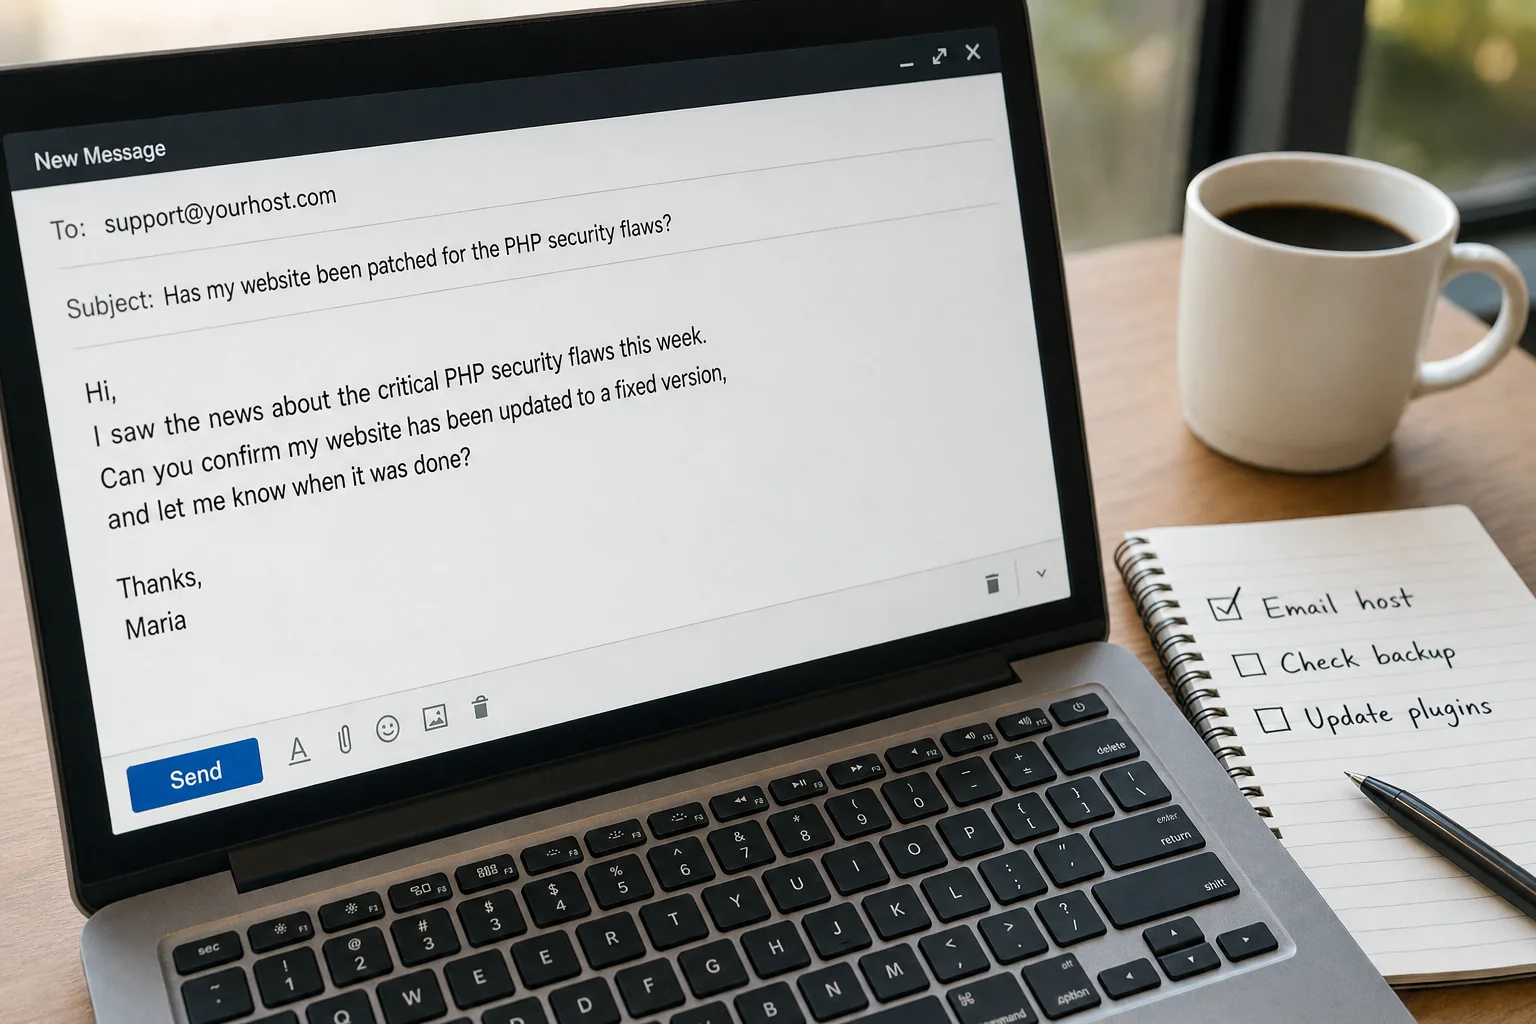
You don't need to understand any of the technical detail. Just send your hosting company or web developer this:
Hi, I saw the news about the critical PHP security flaws this week. Can you confirm my website has been updated to a fixed version, and let me know when it was done?
Then work through this short list:
- Make sure you have a recent backup. Ask your host where it's kept, or install a reputable backup plugin.
- Update everything inside WordPress. WordPress itself, your theme and your plugins. Look for "Updates" in your WordPress dashboard.
- Keep asking until you get a clear "yes". If nobody can give you a straight answer, that's the real problem: nobody is looking after your website.
The bigger picture: a website that needs babysitting
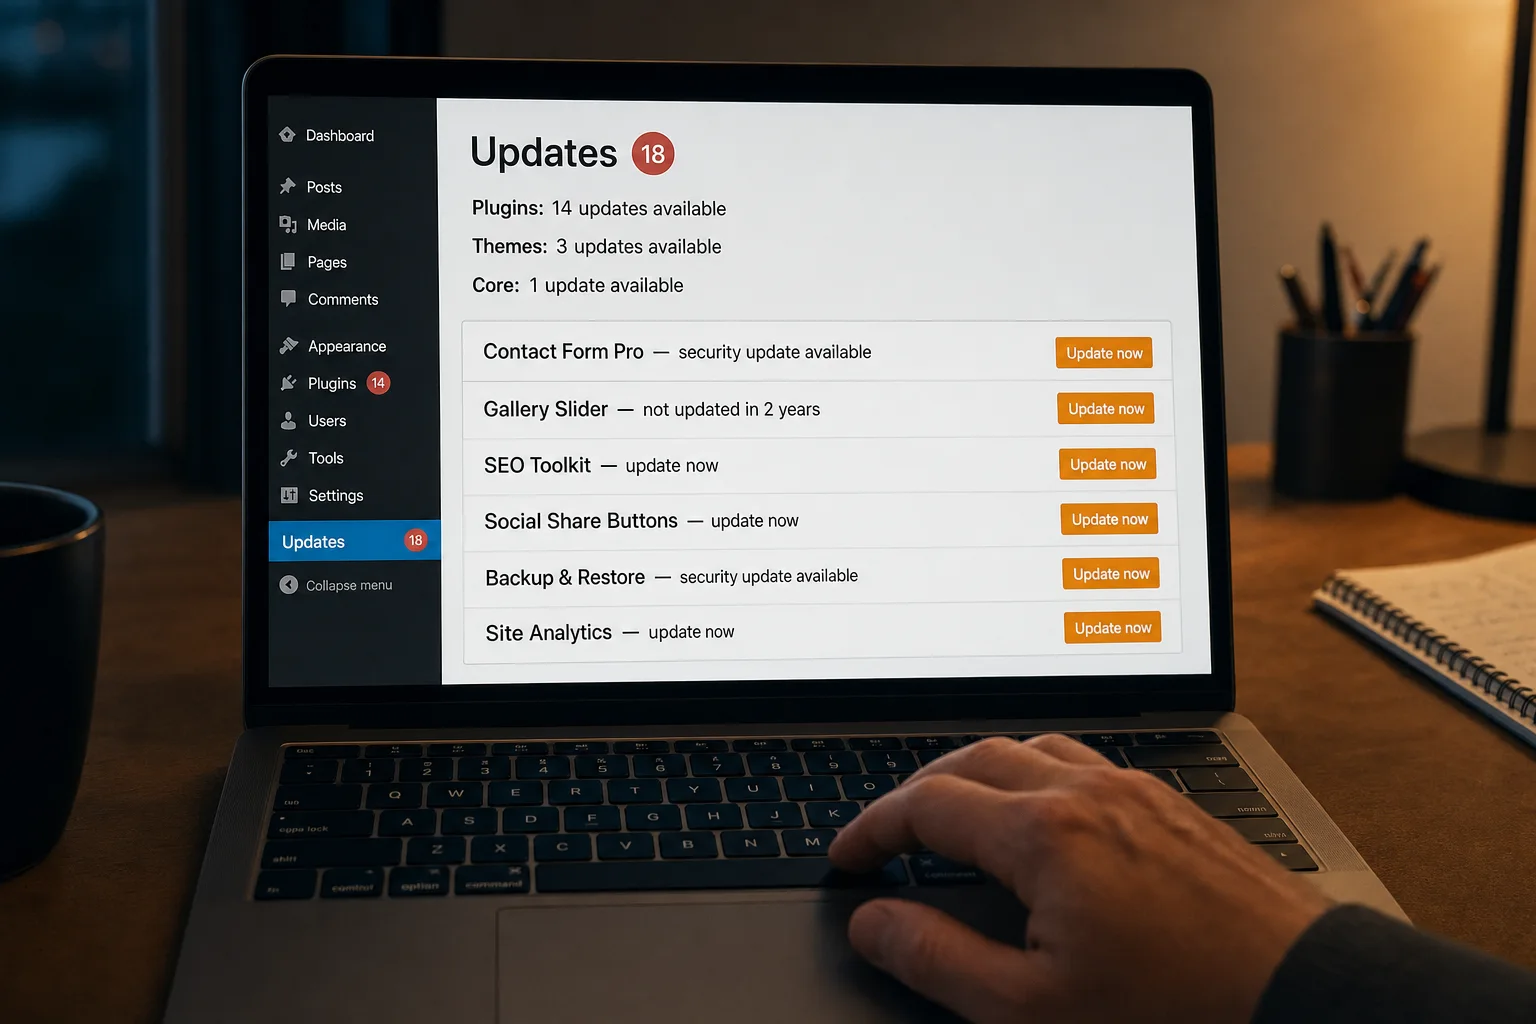
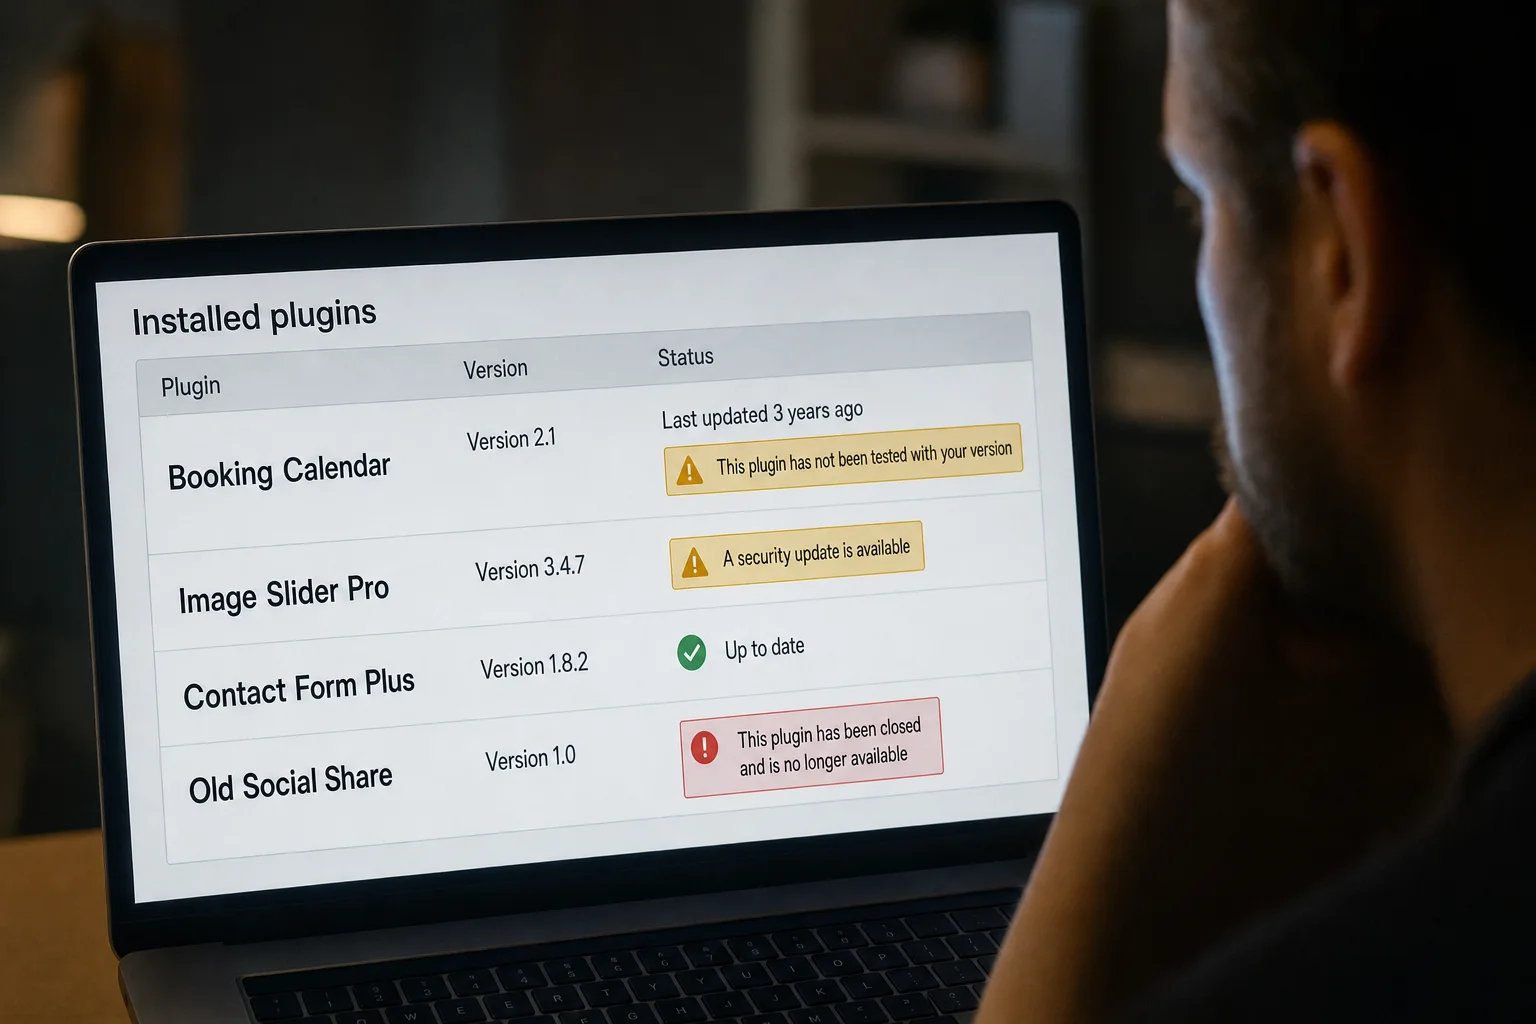
Eighteen updates waiting, and one plugin nobody has touched in two years. This screen is more common than you'd think.
This won't be the last alert like this. WordPress is powerful and popular, but a typical WordPress site runs software behind the scenes every time someone visits. That's WordPress itself, your theme and, often, twenty or more plugins. Each one comes from a different company, and each one needs updating.
Think of each piece as a door into your website. Every so often a weakness turns up in one, and somebody has to go round and fix it. On a self-hosted WordPress site, that somebody is usually you.
For a florist or a dental practice, that's a job nobody signed up for.
Or skip the job entirely. A Mondovo site has no PHP version to chase your host about, no WordPress core, theme or plugins to update, and no backups to take. Pages are published as finished files from a global network, and keeping the platform secure is our job. To see your own business there first, try Mondovo free: paste your current address and it builds three designs from your own pages.
What are the alternatives?
If you'd rather not think about security alerts at all, you have three options:
- Pay for fully managed WordPress hosting. You keep WordPress, and the host takes care of updates. Plugins can still cause problems, and you still depend on someone else doing the work.
- Move to an all-in-one website builder. The platform looks after security, so there's nothing for you to patch.
- Choose a platform that publishes "static" websites. Your pages are prepared in advance and delivered as finished files. Nothing is running behind the scenes when a visitor arrives, so there's far less for an attacker to break into.
No website is ever 100% risk-free. But the fewer moving parts, the fewer of these alerts you have to read.
Why a Mondovo site shrugs this one off
We built Mondovo around that last idea. Every Mondovo site is published as finished pages from a fast global network. There's no WordPress, no plugins, no PHP and no server software for you to look after, and no backups to manage. Hosting, SSL and platform security are our job, not yours.
So when an alert like this one makes the news, there's no email to send and nothing you need to do. Forms with an enquiry inbox, bookings, an online store and email are built into Mondovo, so you don't miss the plugins either. If your site depends on a niche plugin, check first: Mondovo is younger than WordPress and has no plugin directory.
Moving your WordPress site to Mondovo
You don't have to start from scratch, and nothing changes on your current site while you try it:
- Paste your current web address. Nothing to install on your WordPress site, no passwords to hand over.
- Mondovo brings your pages, posts and images across, along with your logo, brand colours and the structure of your site.
- You review the plan before any design is made.
- You get three fresh designs built with your own content, and pick the one you like.
- You go live when you're ready, on your own domain. Every old page address, including WordPress-style links, is redirected to the closest new page, so links in Google keep working. Anything that didn't match exactly is flagged for you to check.
Forms, bookings and payments work on Mondovo, but they're set up again rather than moved from your old plugins. Members-only content and a shop's order history don't come across either. The WordPress migration page covers exactly what comes across and what doesn't.
Building your new site on Mondovo is free, so you can see it before you decide anything. Going live is $20 a month on Pro, hosting and SSL included.
Move my WordPress site to Mondovo → or start building free.
More on this: Is WordPress secure? and What to do if your WordPress site is hacked.
Details checked on 21 October 2026, the day the PHP fix came out.
Frequently asked questions
What is PHP, and why does it matter for my WordPress site?
PHP is the software WordPress runs on, provided by your hosting company. If PHP has a serious flaw and your host hasn't installed the fix, your site can be at risk even if WordPress itself is up to date.
Is my WordPress site affected by the PHP flaws?
It depends on whether your host or developer has installed the fix released on 21 October 2026. The quickest way to find out is to email them and ask for a clear yes, and when it was done.
Can I install the PHP fix myself?
Usually not. On most hosting plans PHP is managed by the host. What you can do is update WordPress, your theme and plugins, and make sure you have a recent backup.
Is there a website platform that doesn't need security updates?
No website is risk-free, but on some platforms the updates aren't your job. On Mondovo there's no core, theme, plugin or PHP for you to update and no backups to manage. Pages are static files from a global network, and platform security is ours to handle.